Best Contract Management Software for Financial Services (2026)
Financial services contracts are among the most demanding in any industry. Every agreement carries regulatory weight. Loan documents must comply with SEC disclosure requirements. Investment management contracts need MiFID II alignment. Vendor agreements must address operational resilience under OCC and FFIEC guidelines. KYC and AML obligations get embedded directly into client onboarding contracts. And every change, every approval, every version must produce an audit trail that can withstand a regulatory examination years later.
The result: financial services firms manage more contract complexity per agreement than nearly any other sector. A single client onboarding can involve NDAs, engagement letters, service agreements, compliance addenda, and data processing agreements, all subject to overlapping regulatory frameworks including Dodd-Frank, FINRA rules, Basel III requirements, and state-level regulations. When something goes wrong, the consequences are not just commercial. They are regulatory.
This guide evaluates 8 CLM platforms against the specific requirements financial services firms face. We looked at compliance infrastructure, audit trail depth, regulatory clause management, integration with financial systems, and whether each tool can actually handle the multi-party, multi-jurisdictional nature of financial contracts.
How We Evaluated
We assessed each platform across six dimensions specific to financial services: regulatory compliance capabilities (audit trails, access controls, retention policies), contract intelligence for financial terms, integration with financial systems, implementation complexity, pricing transparency, and real-world suitability by firm size. We consulted G2, Capterra, and Gartner reviews, vendor documentation, and verified third-party pricing data where public pricing was unavailable.
Transparency Note
Bind is our product. We include it in this guide and hold it to the same criteria as every other tool. Where Bind falls short for financial services use cases, we say so. Large banks with complex regulatory reporting requirements may need a specialized platform. We believe honest comparison is more useful than marketing spin.
Why Financial Services Contracts Need Specialized Tools
Contract management in financial services is not simply a more complex version of general contract management. The regulatory environment creates requirements that most CLM platforms were never designed to handle.
Regulatory Overlay on Every Agreement
Financial services contracts operate under multiple simultaneous regulatory frameworks. A single investment advisory agreement may need to satisfy SEC Rule 206(4)-7 (compliance programs), FINRA Rule 3110 (supervision), the Investment Advisers Act, and applicable state securities laws. Vendor contracts must address OCC third-party risk management guidelines and increasingly, DORA (Digital Operational Resilience Act) for firms with European operations.
Most general-purpose CLMs treat compliance as a checkbox. Financial services firms need compliance woven into clause libraries, approval workflows, and post-execution monitoring. For tools specifically built around contract compliance tracking and reporting, see our dedicated guide.
Audit Trail Requirements
When regulators examine a financial institution, they do not just look at the final signed contract. They want to see who drafted it, who reviewed it, what changed between versions, who approved each change, and when. A complete audit trail is not optional. It is a regulatory requirement under multiple frameworks including SOX Section 404, FINRA Rule 4511, and SEC Rule 17a-4.
SOC 2, ISO 27001 and DORA: what to ask a CLM vendor
A CLM that meets SOC 2 and financial regulations is really two separate questions. SOC 2 and ISO 27001 are about the vendor's own security. SOC 2 is an independent auditor's report on a provider's controls: Type I confirms the controls were suitably designed at a point in time, Type II that they operated effectively over a period, typically three to twelve months. Ask for the current report under NDA and read the exceptions, not only the cover page. ISO 27001 is a certification of the vendor's information security management system.
Financial regulation is about your obligations, and no certificate transfers them to a vendor. For EU financial entities, DORA has applied since 17 January 2025 and requires contracts with ICT providers to include specific provisions, among them a clear description of the services, service levels, and termination rights with notice periods. Where the service supports a critical or important function, the contract must also give rights of access, inspection and audit, and support for an orderly exit. A CLM is itself an ICT service under that regime, so its contract with you needs those terms, and it can also help you check that your other vendor contracts carry them.
So ask each vendor for three things: its SOC 2 report and ISO 27001 certificate, where data is hosted and which subprocessors are used, and whether its standard agreement includes the audit, termination and exit terms a regulated firm needs. Bind is ISO 27001 certified and holds a SOC 2 Type I report.
Multi-Party Complexity
Financial transactions routinely involve three or more parties. Syndicated loans can have dozens of participants. Fund formation documents involve general partners, limited partners, administrators, and counsel. M&A transactions produce cascading contract requirements across multiple entities and jurisdictions. The CLM must handle these multi-party structures without breaking version control or audit integrity.
KYC/AML Integration
Client contracts in financial services are not just commercial agreements. They are part of the compliance infrastructure. Client onboarding contracts must capture KYC representations, AML certifications, beneficial ownership disclosures, and tax status declarations. The CLM should connect this contract data to compliance systems rather than treating it as isolated text.
1Client Onboarding and KYC
2Contract Drafting with Regulatory Clauses
3Internal Compliance Review
4Multi-Party Negotiation
5Execution with Full Audit Trail
6Ongoing Obligation Monitoring
7Regulatory Reporting and Renewal
Generic CLM
Basic audit trail (who signed, when)
Standard clause library
Manual compliance checking
Single-party or two-party workflows
General document storage
Calendar-based renewal reminders
Financial-Services-Ready CLM
Full version history with user, timestamp, and change detail on every action
Regulatory clause libraries (SEC, FINRA, MiFID II, Dodd-Frank)
Automated compliance checks against internal policies and regulatory requirements
Multi-party workflows with role-based access and approval chains
Retention policies aligned with regulatory requirements (SEC 17a-4, FINRA 4511)
Proactive obligation monitoring with regulatory deadline tracking
Best for: Large financial institutions with complex regulatory requirements across multiple jurisdictions
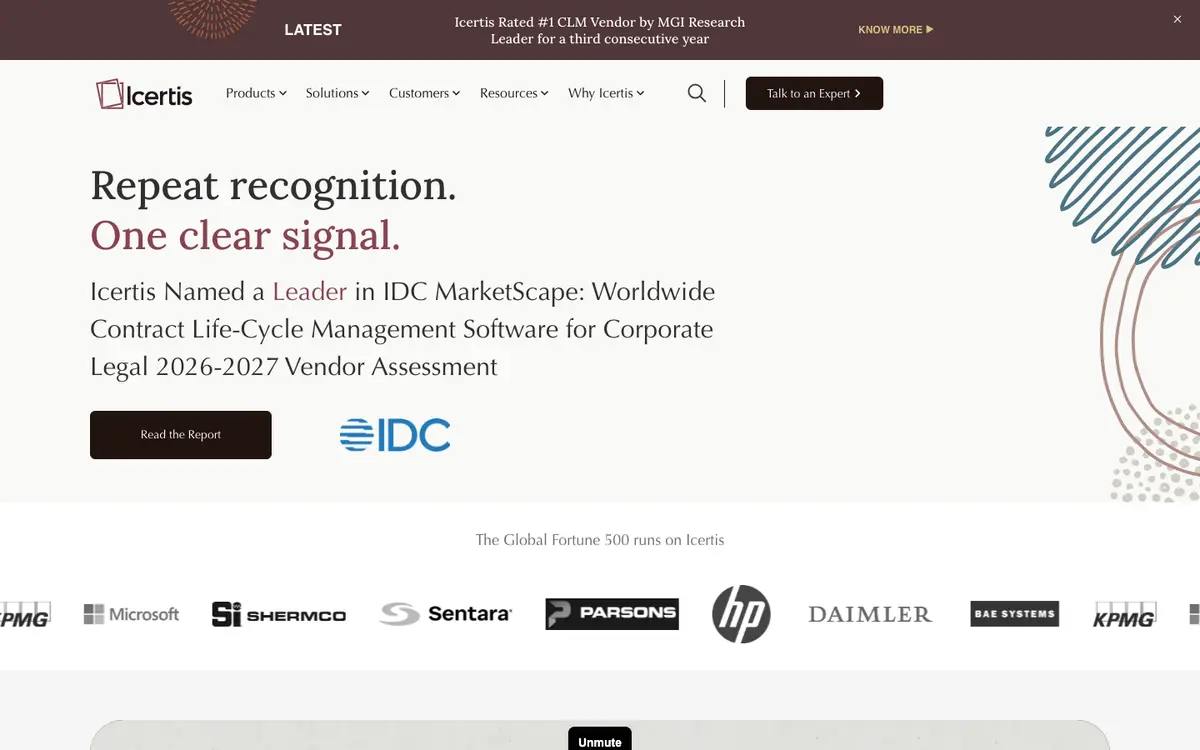
Pricing: Custom-quoted; Icertis publishes no rate card | G2: 4.2/5
Icertis homepage, November 2026
Icertis Contract Intelligence (ICI) is the enterprise CLM most commonly deployed at large financial institutions. It treats contracts as structured data, extracting obligations, risk factors, financial terms and compliance requirements across an entire portfolio. About 70% of its G2 reviews come from companies with 1,000+ employees, which reflects its true target market.
For financial services, the contract intelligence layer is the differentiator. Icertis continuously analyzes the portfolio for regulatory compliance gaps, obligation conflicts and renegotiation opportunities across thousands of agreements. For a global bank managing counterparty agreements across 30 countries under different regulatory regimes, that portfolio-level view is genuinely valuable. It also covers revenue recognition alignment, billing term enforcement and financial risk scoring, with regulatory clause libraries for major financial frameworks.
Key Features:
Contract intelligence engine that turns contracts into structured, analyzable data
AI-powered risk identification and continuous compliance monitoring
Obligation tracking with regulatory deadline awareness across portfolios
Enterprise-grade security certifications for regulated industries
Limitations:
Priced at the enterprise end of the market; Icertis publishes no rates, so budget on a quote rather than a benchmark
Deployments are configuration projects rather than switch-ons, and no vendor publishes a timeline
Recurring G2 review themes describe the interface as complex and hard to learn
Reliance on implementation partners adds to total cost of ownership
In practice: Icertis is what global banks, insurance conglomerates and large asset managers deploy to manage regulatory compliance across tens of thousands of contracts in multiple jurisdictions. Smaller and mid-market firms should weigh the cost and implementation effort against how much of that portfolio-scale capability they will actually use.
Bind
Best for: Mid-market financial services firms wanting AI-native CLM without enterprise pricing
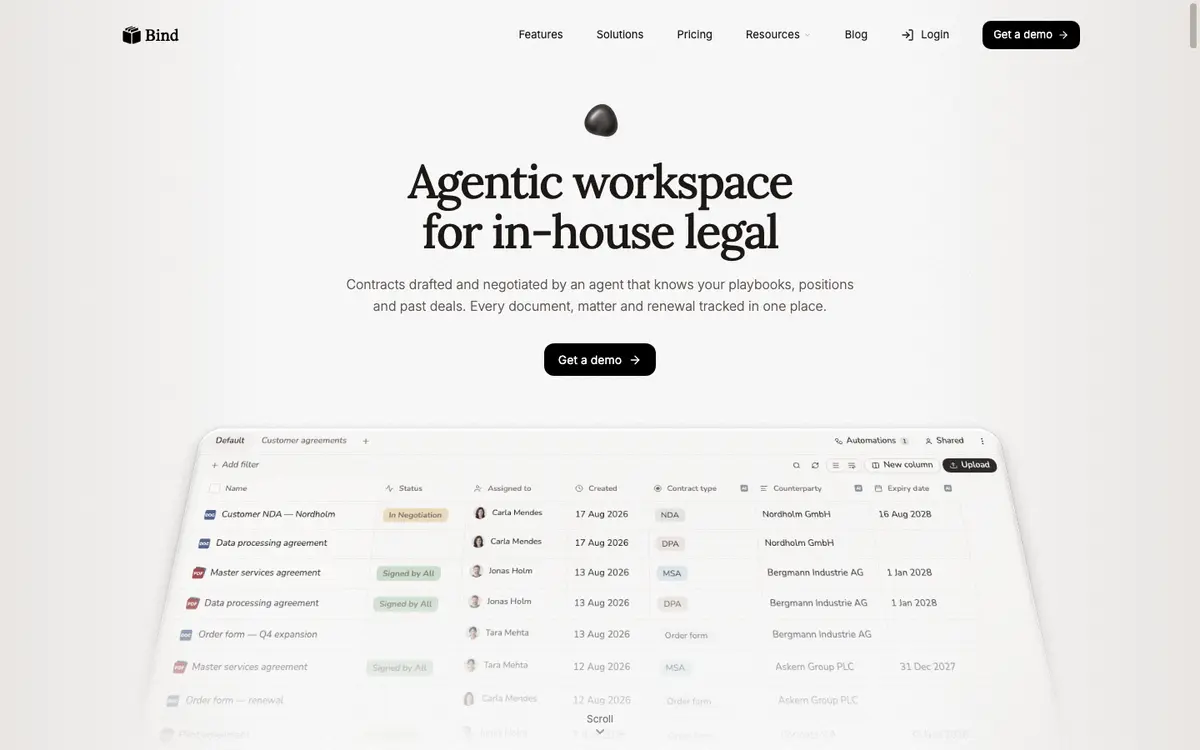
Bind is an AI workspace for in-house legal teams: drafting, review, negotiation, e-signature and contract management in one product, with an audit trail on every action. For financial services firms it replaces the mix of Word files, separate e-signature tools and shared drives many mid-market firms still use.
Describe the agreement, including regulatory requirements, and Bind drafts it from its built-in template library: loan, service and vendor agreements, NDAs, engagement letters and compliance addenda. The Business tier adds playbook automation, which flags deviations from your approved compliance terms. Semantic search and the Tabula view (custom columns and filters) cover the portfolio.
For examination prep, counsel can ask Claude or ChatGPT "Which of our vendor contracts give us audit rights?" through Bind MCP and get linked answers. Bind MCP is read only, uses each person's own Bind login and logs every document it reads. A GRC tool can pull dates and fields through the Bind API with a Read key for one space; both come on every plan.
Strengths:
Replaces 4-5 separate tools in one platform
Published per-seat pricing where most CLMs are custom-quoted
Operational within a day in our own deployments, no consultants
Limitations:
Newer, smaller customer base; first two reviews on G2, too few to judge by
No SOX-specific modules, automated regulatory reporting or FINRA/SEC filing integrations
Playbooks and AI review need the Business tier; large multi-jurisdictional banks may need Icertis
In practice: Bind is used by in-house legal teams at listed companies including Atria (Nasdaq Helsinki) and Outdoor Holding (Nasdaq US), and by Slush. It fits mid-market financial firms, advisory boutiques and fintechs with hundreds of contracts rather than thousands, under general rather than banking-specific regulation.
Best for: Financial services companies needing sophisticated workflow automation for contract approvals
Pricing: Custom pricing; Ironclad publishes no rates and Vendr reports contracts at a median of about $40,492/year across 372 purchases (range $15,000-$106,988) | G2: 4.5/5
Ironclad homepage, November 2026
Ironclad is the CLM most associated with workflow automation. Named a Leader in the 2025 Gartner Magic Quadrant for CLM (published November 2025), it is built for legal teams whose contracts pass through complex approval chains with conditional logic.
That matters in financial services, where approvals are rarely simple. A new client agreement might route to compliance for regulatory review, to risk for counterparty assessment, to a managing director for commercial approval and to legal for sign-off, with routing that changes by deal size, product type and client jurisdiction. Ironclad's Workflow Designer handles these multi-branch processes natively, with audit trails built into every step. The Salesforce integration is particularly deep: contracts are generated from Salesforce records and contract data flows back into the CRM.
Key Features:
Visual Workflow Designer for multi-step, conditional approval chains
AI-assisted contract review (Ironclad AI)
Deep Salesforce integration with bidirectional data mapping
Post-signature repository with reporting and obligation tracking
Limitations:
Custom-quoted with no published rates; Vendr reports a median of about $40,492/year across 372 purchases (range $15,000-$106,988), well above self-serve tools
Steep learning curve for non-legal users is a recurring theme in G2 reviews
Ironclad publishes no implementation timeline; deployments are faster to stand up than enterprise CLM
Editing is centred on Word rather than a browser-native editor, a workflow preference to test in a trial
Ironclad has shipped an agentic AI suite; if AI redlining is the priority, compare it head-to-head against AI-native platforms
In practice: Ironclad suits mid-to-large financial services firms that have outgrown simpler tools and route contracts through compliance, risk and legal with different rules for different agreement types.
Agiloft
Best for: Financial firms needing deep customization to match unique internal processes
Pricing: Custom-quoted; Agiloft publishes no rate card. Vendr median ~$67,132/yr (range $62,629-$80,344) | G2: 4.6/5
Agiloft homepage, November 2026
Agiloft is the most configurable CLM available. Named a Leader in the 2025 Gartner Magic Quadrant for CLM, it provides a no-code environment where administrators customize workflows, fields, approval logic, dashboards and virtually every other part of the system.
Financial institutions often have contract workflows shaped by years of regulation and internal policy. A derivatives trading desk, a retail banking unit and a wealth management division might each follow completely different processes, and Agiloft can model all three in one system. The ConvoAI feature adds AI-assisted contract review. Agiloft does not publish rates, but per Vendr's purchasing data the median contract is about $67,132/year (range $62,629-$80,344), firmly enterprise budget territory.
Key Features:
No-code workflow and field configuration for complete process customization
ConvoAI for AI-assisted contract review and risk identification
Customizable dashboards, reporting and compliance views
Strong obligation tracking and deadline management
Strengths:
Compliance and operations teams can build their own processes without code
Configuration scope, not headcount, drives the quote, so the platform can be sized very differently
Limitations:
Recurring G2 review themes describe the interface as less modern than browser-native competitors like Juro and Bind
Initial configuration commonly involves implementation consultants, adding to total cost
Steep learning curve for teams without a dedicated admin is a recurring review theme
Without strong governance, configurations get harder to maintain
In practice: Agiloft is the right choice for financial firms with compliance or operations teams willing to invest in configuration. The payoff is a system that matches your exact processes, but the investment in time and administrative overhead is real.
LinkSquares
Best for: Extracting intelligence from existing financial agreements and building a searchable contract database
Pricing: Custom-quoted; Vendr median ~$31,000/yr across 152 purchases (range $5,999-$79,200) | G2: 4.7/5
LinkSquares homepage, November 2026
LinkSquares focuses on contracts that are already signed. Its Analyze module automatically extracts 75+ data points from existing contracts, surfacing renewal dates, obligations, risk factors and financial terms. For financial services firms sitting on thousands of signed agreements with no central view of what is inside them, this is genuinely valuable.
LinkSquares reports being named a G2 Leader for 17 consecutive quarters, with most of its G2 reviewers rating it 4 or 5 stars. It recently announced agentic AI capabilities and an AI-powered risk scoring agent. Upload vendor agreements, counterparty contracts and SLAs, and it builds a searchable database: when a regulator asks for every contract with a specific indemnification structure, or risk needs every agreement expiring in the next 90 days, the data is immediately accessible.
Key Features:
Automated extraction of 75+ data points from signed agreements
Two modules: Finalize (pre-signature) and Analyze (post-signature)
AI-powered risk scoring agent for contract risk assessment
Agentic AI with natural language queries across extracted data
Limitations:
Recurring G2 review themes note that extraction accuracy drops on layered indemnity structures and heavily amended contracts
The centre of gravity is post-signature analysis; evaluate the pre-signature module carefully if authoring is your main need
Reviewers report that search does not handle misspellings well or prioritize results as expected
Check the integration catalogue against your stack; reviewers as of our August 2026 review noted gaps in workflow-tool connectors
In practice: LinkSquares is the right choice when the main problem is understanding what is already in the portfolio: hundreds of vendor, client and counterparty documents with no central visibility into terms, obligations and renewal dates. For strong drafting, negotiation and compliance review, pair it with a tool that handles those stages better.
Juro
Best for: Mid-market fintech and financial services firms wanting modern UX and collaborative negotiation
Pricing: Custom pricing; Juro publishes no rates, so confirm the figure for your team size directly | G2: 4.8/5
Juro homepage, November 2026
Juro is a browser-native CLM that removes the Word dependency common in financial services. Contracts are drafted, negotiated and signed in a rich-text editor in the browser, and both parties negotiate in a shared environment with real-time visibility, instead of emailing files and re-importing tracked changes.
Juro holds the highest G2 rating (4.8/5) among mid-market CLM tools and scores 5.0/5.0 for customer support. Its AI Extract feature identifies renewal dates, notice periods, billing cycles and payment terms from uploaded contracts, removing manual data entry for finance teams. Backed by $32 million in venture capital from Fidelity, USV and the founders of Indeed, Wise and Gumtree, Juro has strong traction in fintech.
Key Features:
Browser-native editor with real-time collaborative negotiation
AI Assistant for drafting, reviewing and summarizing contracts
AI Extract for financial terms and deadlines, driving renewal reminders
Juro has marketed unlimited users on its plans; confirm the seat terms in your own quote
Strengths:
Among the fastest implementation times in the CLM category according to G2 data
An unlimited-user model, where offered, keeps costs flat as teams grow
Limitations:
Recurring G2 review themes describe templates and workflows as harder to bend when contract types deviate from standard structures
As of our August 2026 review, Juro's AI centres on drafting assistance and data extraction rather than financial-regulatory risk analysis; confirm current capabilities with the vendor
No public pricing page; budgeting requires a sales conversation
In practice: Juro fits fintechs and mid-market financial firms where collaborative negotiation speed matters more than deep regulatory compliance automation, and where compliance, legal and business teams all need contract access.
SpotDraft
Best for: Fast-growing fintech companies with active legal teams
Pricing: Custom pricing (subscription-based, user or volume model) | G2: 4.6/5
SpotDraft homepage, November 2026
SpotDraft is an AI-native CLM built for fast-growing companies, with clients including Airbnb, Notion and Strava. It provides centralized contract storage, customizable approval workflows, e-signature integration and the SpotInsights dashboard for lifecycle analytics.
VerifAI, SpotDraft's AI review feature, checks contracts against organizational standards and flags deviations, so financial services firms can encode compliance requirements into review. Guided workflows centralize pre-approved clauses, dynamic templates, fallback playbooks and approval rules. Per SpotDraft's own published materials, the company raised $54 million in Series B funding and serves several hundred customers.
Key Features:
AI-powered review (VerifAI) against organizational standards
SpotInsights dashboard for lifecycle visualization and bottleneck identification
Guided workflows with centralized clause libraries and fallback playbooks
Flexible pricing: user-based or volume-based models
Strengths:
Clean, modern interface with good adoption among non-legal users
Flexible pricing accommodates different fintech business models and growth stages
Limitations:
Some G2 reviewers report that template edits and configuration changes involve the support team
As of our August 2026 review, test VerifAI against your most complex financial regulatory contracts before relying on it there
Newer modules such as VerifAI may be priced separately; confirm bundling in your quote
No publicly available pricing
In practice: SpotDraft works well for fintechs and growth-stage financial firms where legal drives contract operations and needs lifecycle visibility. For the most complex regulatory requirements it may not go deep enough, but it covers most fintech use cases well.
Concord
Best for: Smaller financial services firms and advisory practices needing simple, affordable CLM
Pricing: Per Concord's published pricing as of August 2026: plans start at a $499/month for 5 users; higher tiers and Enterprise are quoted separately
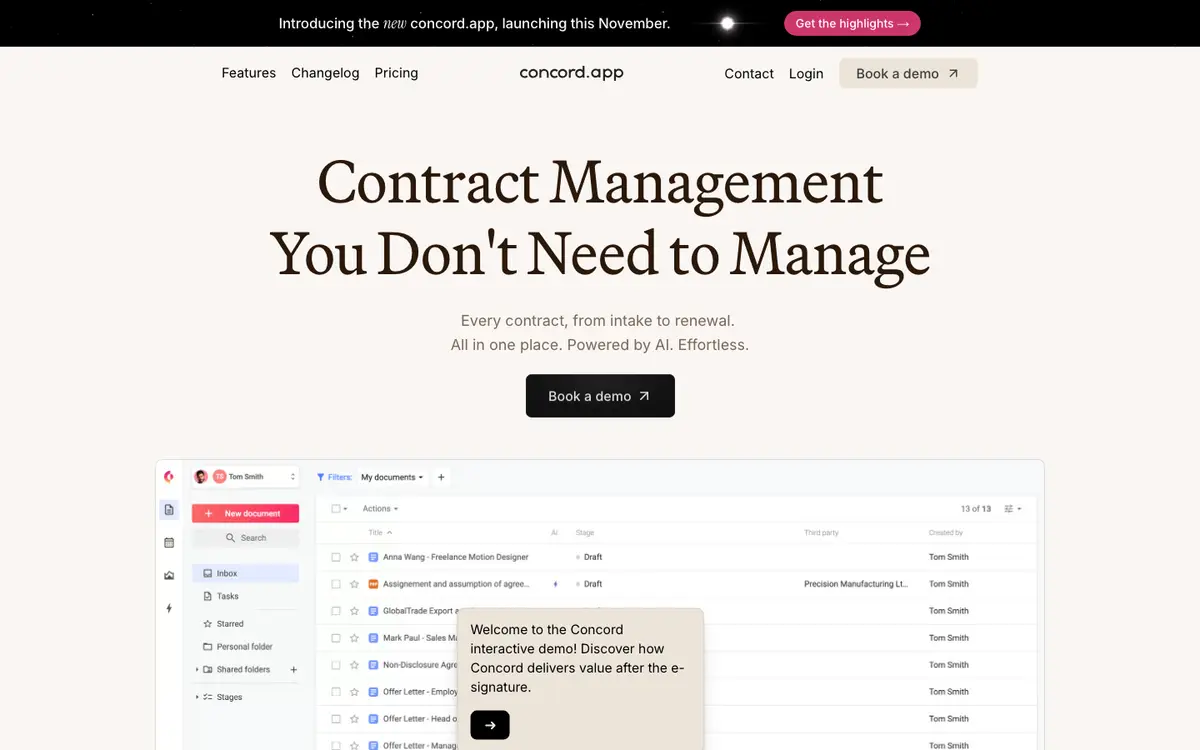
Concord homepage, November 2026
Concord is a CLM built around simplicity and transparent pricing. All plans include unlimited documents and e-signatures, AI Copilot and extraction, and full audit trails. For smaller financial firms, advisory practices and boutique investment firms, it provides core contract management without enterprise complexity.
Concord Horizon, introduced in 2026, adds a conversational AI interface. Multi-party signing handles agreements that need three or more signatories, common in transactions with multiple counterparties. At a published $499 per month with unlimited documents, a five-person advisory firm sending 30 contracts a month pays the same as one sending 300.
Key Features:
Unlimited documents and e-signatures on all plans
AI Copilot and extraction for contract analysis
Multi-party signing for agreements with three or more signatories
Approval workflows with conditional routing and full audit trail
Limitations:
Recurring G2 review themes describe template management and the Word import experience as a weak point
Reviewers report that the signing experience restricts signature placement to predetermined areas
Mobile support is limited; check Concord's current app availability if field access matters
Integrations vary by plan tier; confirm which connectors your tier includes
Not built around the deep regulatory compliance tooling larger financial institutions need
In practice: Concord is the right choice for smaller financial firms that want contracts drafted, signed and stored with audit trails at a published flat monthly rate. Firms with complex regulatory requirements, multi-jurisdictional operations or advanced compliance automation needs will outgrow it.
How to Choose the Right CLM for Your Financial Services Firm
The right platform depends on your firm's size, regulatory complexity, and primary contract pain point. Here are decision frameworks that map to real financial services scenarios.
By Firm Size
Firm Size
Annual Revenue
Recommended Tools
Why
Boutique advisory (2-15 people)
Under $10M
Bind, Concord
Affordable, fast setup, covers core needs without enterprise overhead
Mid-market firm (15-200 people)
$10M-$500M
Bind (Business), Juro, SpotDraft
Balance of capability, compliance features, and reasonable pricing
Large institution (200-1,000 people)
$500M-$5B
Ironclad, Agiloft, LinkSquares
Advanced workflows, deep customization, post-execution analytics
(These are our own fit recommendations, not vendor-stated market segments. Placing a vendor in one row does not mean it is unavailable to smaller firms, so ask for the tier that matches your size rather than assuming.)
By Budget
Monthly Budget
Best Options
Notes
Under $500/month
Bind (Starter), Concord
Both include audit trails and unlimited documents
$500-$2,500/month
Bind (Business), Juro, SpotDraft
Compliance automation and AI review capabilities
$2,500-$10,000/month
Ironclad, Agiloft, LinkSquares
Advanced workflows, deep customization, portfolio analytics
$10,000+/month
Icertis
Enterprise regulatory compliance at scale
(Bind and Concord figures are published rates. The other platforms are custom-quoted and publish no rates, so their placement here reflects Vendr's purchasing data rather than vendor-stated prices, and any vendor may quote outside these bands.)
By Primary Need
Primary Need
Best Tool
Runner-Up
Fast contract creation with compliance guardrails
Bind
Juro
Complex multi-department approval workflows
Ironclad
Agiloft
Post-execution obligation tracking and governance
Icertis
LinkSquares
Understanding existing contract portfolio
LinkSquares
Icertis
Maximum configurability for unique processes
Agiloft
Ironclad
Enterprise regulatory compliance at scale
Icertis
Ironclad
Affordable CLM for small financial firms
Concord
Bind (Starter)
Fintech-friendly with collaborative negotiation
Juro
SpotDraft
9%
of the bottom line lost on average to poor contract management
World Commerce & Contracting
World Commerce & Contracting reports that poor contract management costs companies about 9% of their bottom line. For a financial services firm, that leakage shows up as missed renewals, unfavorable terms, compliance gaps, and delayed deals. Even the most expensive CLM on this list costs a fraction of a typical firm's contracting margin.
A CEO's Take on Modern CLM
Evaluating CLM tools is easier when you hear the thinking behind one. Bind CEO Aku Pöllänen explains Bind's approach to the full contract lifecycle:
See how Bind works
Trusted by fast-moving legal teams around the world
What regulatory requirements should financial services CLM software address?
At minimum, your CLM should support compliance with SEC record-keeping requirements (Rule 17a-4 for broker-dealers), FINRA supervision and record retention rules (Rules 3110 and 4511), SOX Section 404 internal controls over financial reporting, and applicable AML/KYC regulations. For firms with European operations, MiFID II transaction reporting and GDPR data processing requirements apply. The most practical way to address this: ensure your CLM produces complete audit trails (who did what, when, and why), supports role-based access controls, and allows configurable retention policies. No CLM automates regulatory filings directly, but the right platform ensures you have the documentation regulators expect to see.
How important is audit trail depth for financial services contracts?
Critical. During a regulatory examination, FINRA or the SEC will expect to see the complete history of a contract: initial draft, every revision, who approved each change, timestamped negotiation records, and the final executed version with signature verification. A CLM that only records "contract signed on date X" is insufficient. Look for platforms that log every action (view, edit, comment, approve, sign) with user identification and timestamps. Bind, Ironclad, and Icertis all document this level of audit detail in their product materials. Concord and Juro publish audit trail capabilities as well; confirm the level of granularity you need directly with each vendor.
Can a general-purpose CLM work for financial services, or do we need an industry-specific tool?
For most mid-market financial firms, a strong general-purpose CLM with good audit trails, compliance workflow capabilities, and robust access controls will work. You do not necessarily need a platform marketed exclusively for financial services. The key is ensuring the tool can handle your specific requirements: multi-party agreements, regulatory clause libraries, configurable approval chains that include compliance review, and retention policies that meet SEC and FINRA requirements. That said, the largest institutions with the most complex regulatory obligations (global banks, large insurance companies, major asset managers) often benefit from platforms like Icertis that have pre-built configurations for financial services.
What is the typical implementation timeline for a financial services CLM?
It varies widely, and no vendor here except us publishes an implementation timeline, so treat any duration you read elsewhere as a competitor's estimate rather than a commitment. Self-service platforms like Concord are self-serve to set up. Bind is the one we can speak to directly: in our own deployments it goes live in days rather than months. Mid-market platforms like Juro and SpotDraft are a lighter lift than enterprise CLM, with the work being template migration, compliance workflow configuration, and user training. Enterprise platforms like Ironclad, Icertis, and Agiloft are configuration projects rather than switch-ons, covering custom workflow design, integration with existing financial systems, data migration from legacy repositories, compliance validation, and phased rollout across departments. Financial services implementations carry more work than other industries because of the additional compliance validation steps required, so ask each vendor for a scoped schedule in writing.
How should financial services firms handle legacy contracts during CLM migration?
Start with a prioritized approach rather than trying to migrate everything at once. First, upload all active contracts (those still in force with ongoing obligations) into the new CLM. Use a tool like LinkSquares to extract key data points from these agreements so you immediately have searchable visibility into renewal dates, obligations, and financial terms. Second, migrate contracts approaching renewal in the next 12 months, as these need active management. Third, archive older executed contracts according to your regulatory retention requirements. Most financial services firms are subject to retention periods of five to seven years (or longer for certain agreement types), so even expired contracts need proper storage with audit trail preservation.
 Icertis
 Bind
 Ironclad
 Agiloft
 Juro
 SpotDraft
 Concord